

A significant vulnerability in a key component of the internet’s infrastructure was unveiled this week, prompting website administrators globally to rush to apply a remedy.
The flaw was located in a segment of the PHP programming language — a widely utilized software described as “the backbone of the internet” by Isaac Privett, a senior penetration tester at the Toronto-based cybersecurity firm Packetlabs.
This vulnerability had persisted for several years, potentially enabling malicious actors to gain access to websites, alter them, and extract sensitive information.
This situation led many to temporarily take their websites offline while they implemented fixes, resulting in some sites — including those associated with the Canadian government — becoming inaccessible.
Here’s what you should know about the PHP programming language, the discovery of this issue, and the severity of the vulnerability.
What is PHP?
PHP is a free, open-source programming language that is extensively utilized on the internet. This technology is overseen by the non-profit PHP Foundation, which comprises a team of volunteer board members and a limited number of developers.
When a user visits a website, various elements, including images, hyperlinks, and color schemes, must be correctly assembled and displayed, according to technology analyst Carmi Levy. PHP is responsible for this task, coordinating these components to bring websites to life, Levy explains.
“PHP operates quietly in the background to ensure that websites transition from fragmented data residing on a server to a fully functional site that users can interact with on their browsers and devices,” stated Levy, based in London, Ontario.
A security breach in the foundational PHP code that powers a large portion of the internet has sparked a global alert, compelling governments and major organizations to take their websites offline. Andrew Chang analyzes how advanced AI discovered the vulnerability — and the ongoing battle between defenders and hackers to secure the system.
(Photo credits: The Canadian Press, Reuters, Adobe Stock and Getty Images)
According to Wiz, one of the cybersecurity firms that helped uncover the issue, approximately 70% of websites utilize PHP, while web technology monitor W3Techs estimates that number to be around 75%.
This extensive usage positions PHP as a “foundational” technology essential for the internet’s operation, Levy noted, which is why a vulnerability within it can have far-reaching implications.
What is the issue, and how was it identified?
A team of researchers from the cybersecurity firms Calif and Wiz published blog posts on Wednesday revealing they had discovered two vulnerabilities in PHP. They were operating under an OpenAI initiative aimed at detecting potential vulnerabilities throughout the internet, including in PHP.
Cybersecurity researcher Ryan Austin from Calif.io, who played a role in pinpointing the issues, recounted that he was aware of a 2004 security incident with PHP and directed OpenAI’s GPT‑5.6 Sol to search for other possible bugs in the same section of PHP’s code.
“A few days later, we were able to uncover something quite significant,” Austin remarked.
The PHP Foundation clarified in a release on Wednesday that both vulnerabilities are located in “areas of PHP that nearly every request interacts with: memory management and error handling.”
Austin elaborated that when PHP encounters an error, it retains memory information that can become corrupted, potentially providing hackers with a means of entry to websites.
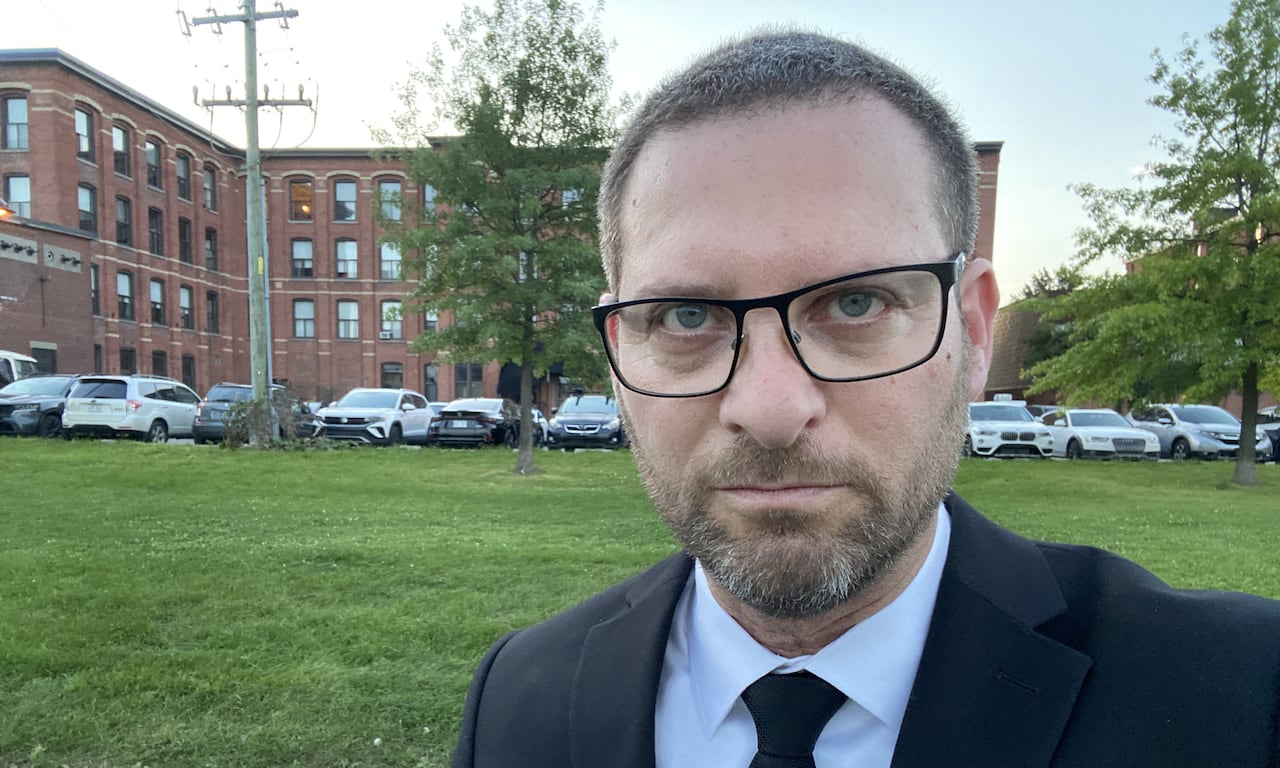
Tech analyst Carmi Levy emphasizes that the widespread use of PHP across the internet amplifies the concern regarding vulnerabilities associated with it. (Submitted by Carmi Levy)
Once hackers breach the system, they could modify websites, potentially inserting malware or removing content, or access confidential information like passwords, according to Levy.
Wiz indicated that these vulnerabilities have been present for over ten years. The PHP Foundation acknowledged that a researcher had speculated about this potential exploit in 2024, but no definitive method to carry it out was identified at that time.
The PHP Foundation stated that the delay in addressing the issue resulted from a “structural failure” tied to resource limitations and the decision-making process of the security team.
How serious is it?
Levy compares the situation to a scenario where a prominent manufacturer of door locks discovers that a master key has become widely accessible.
<p"This means that someone could simply approach your front door, insert that master key, and gain access to your home," Levy explained.
He further noted that security incidents are rated on a scale from zero to ten using the Common Vulnerability Scoring System, with these incidents scoring a 9.2, indicating their seriousness.
Government and corporate websites globally were taken offline after developers identified flaws in the popular PHP code that could expose them to numerous hackers.
Levy stated, “A single vulnerability in a technology that is used by nearly everyone signifies a potential global impact.”
From Austin’s viewpoint, it is “likely one of the most severe vulnerabilities I have ever encountered.”
How is it being resolved?
Cybersecurity professionals report that the positive aspect is that a resolution is available.
The PHP Foundation issued patches for the vulnerabilities on Wednesday and urged users to implement the fixes without delay.
Cybersecurity agencies and government officials globally, including in Canada, echoed this recommendation.
A programmer engages with PHP code at RK Solutions software development firm in Guernica, Spain, on Thursday. (Vincent West/Reuters)
Numerous websites, including those of governmental bodies in Canada, France, and Japan, were temporarily taken offline while the security issue was addressed. For instance, the provincial websites for Newfoundland and Labrador and Prince Edward Island were unavailable for the day, but both appeared to be operational again by Thursday.
The U.S. National Security Agency’s cyber unit advised any organizations that could not promptly apply the fix to take their websites offline until the remedy was implemented.
Although the temporary shutdown of websites caused some concern, Levy points out the situation has a positive aspect. These sites were taken down as a precaution after researchers identified the vulnerability prior to hackers, demonstrating that the system for flagging these issues is functioning effectively.
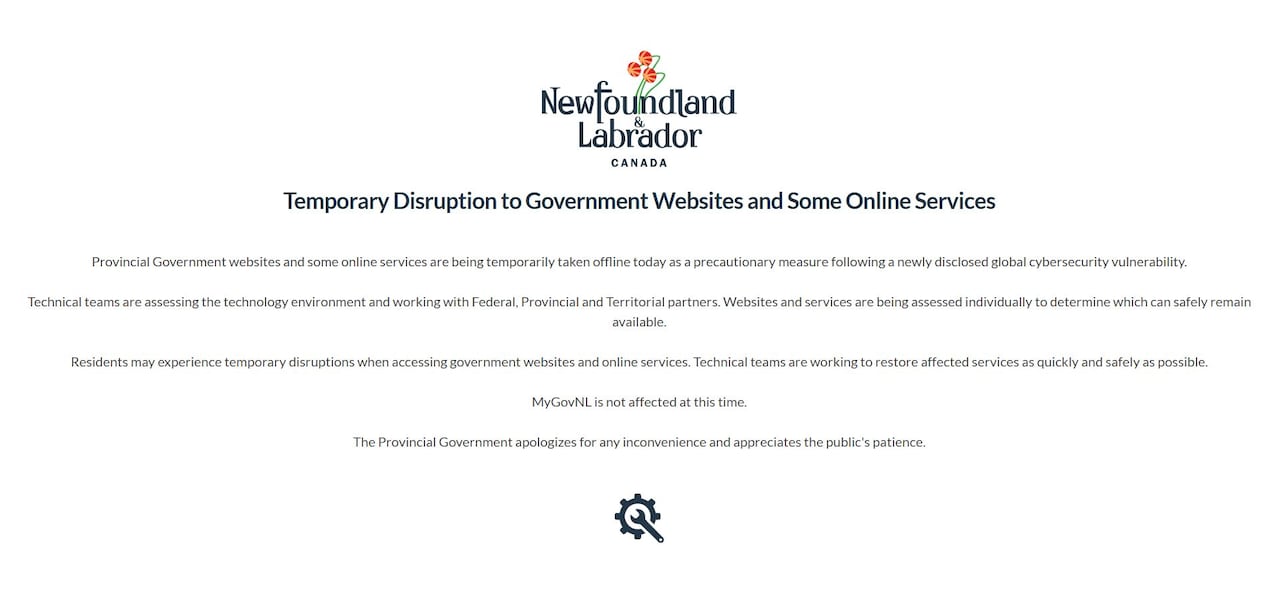
The Newfoundland and Labrador government website was offline on Wednesday due to the disclosed PHP vulnerabilities. (CBC)
Some websites experienced hacking attempts following the vulnerability’s public disclosure, although these attempts did not appear to be successful. For instance, the CEO of Cloudflare reported on social media that their network faced tens of thousands of attempts to exploit the flaw within 45 minutes of the announcement, with “hundreds of thousands” occurring within a two-hour timeframe.
On Wednesday, the PHP Foundation informed CBC News via email that they had not observed any evidence of hackers successfully exploiting the vulnerability.
Should I take any action?
Cybersecurity experts indicate that since the issue affects the backend of websites, the responsibility primarily lies with those managing them — such as businesses or organizations — to ensure the implementation of the fix.
For most website operators, this task is relatively straightforward, similar to updating a personal computer, according to Privett from Packetlabs.
“You simply need to upgrade to the latest version of PHP, which should resolve 99% of your issues,” Privett stated.
A new EY report suggests AI will become a significant factor in cybercrime by 2026 as programs assist attackers in honing their skills.
However, since both the vulnerability and the fix have been publicly disclosed for a while, Privett advises website owners to monitor for signs of possible intrusions that may have occurred before they could implement the patches.
“After you apply the fix, it’s wise to look for indicators of compromise to verify if someone managed to infiltrate your system using that vulnerability,” Privett suggested.
Privett also recommends that individuals who operate their own websites or applications check whether PHP is utilized to ensure they are safeguarded.
For all consumers, Levy emphasizes that they can bolster their protection against potential data breaches by enhancing their personal digital safety measures. Regularly changing passwords, avoiding password reuse, and enabling two-factor authentication, for example, can help ensure that even if hackers access data from a compromised website, they will have a harder time exploiting that information against the user.